
by A2G Spectrum
Consultant-led audit delivery, engineered
Certification you can prove — not just claim
GoMekr runs your ISO 27001, SOC 2 and every other audit as an engineered engagement: a dependency-driven roadmap, decision gates signed by both sides, and evidence health computed from real collection data. Delivered by A2G Spectrum's experts, visible to your leadership every step.
Two decades of audit practice, distilled into one platform — the same methodology that has taken enterprises from first gap assessment to certificate since 2005.
ISO 27001:2022 — ISMS Certification
Sponsor view · live
64%
Active now
7
Overdue
1
Evidence
82%
41
activities in the ISO 27001 roadmap
8
decision gates with dual sign-off
19
evidence sufficiency rules
93
Annex A controls managed
See the platform
The dashboards your team and your clients actually work in
Not mock-ups — the shipping product. One platform, three faces: the firm-side portfolio that runs every engagement, the client compliance home, and focused workspaces per service line.
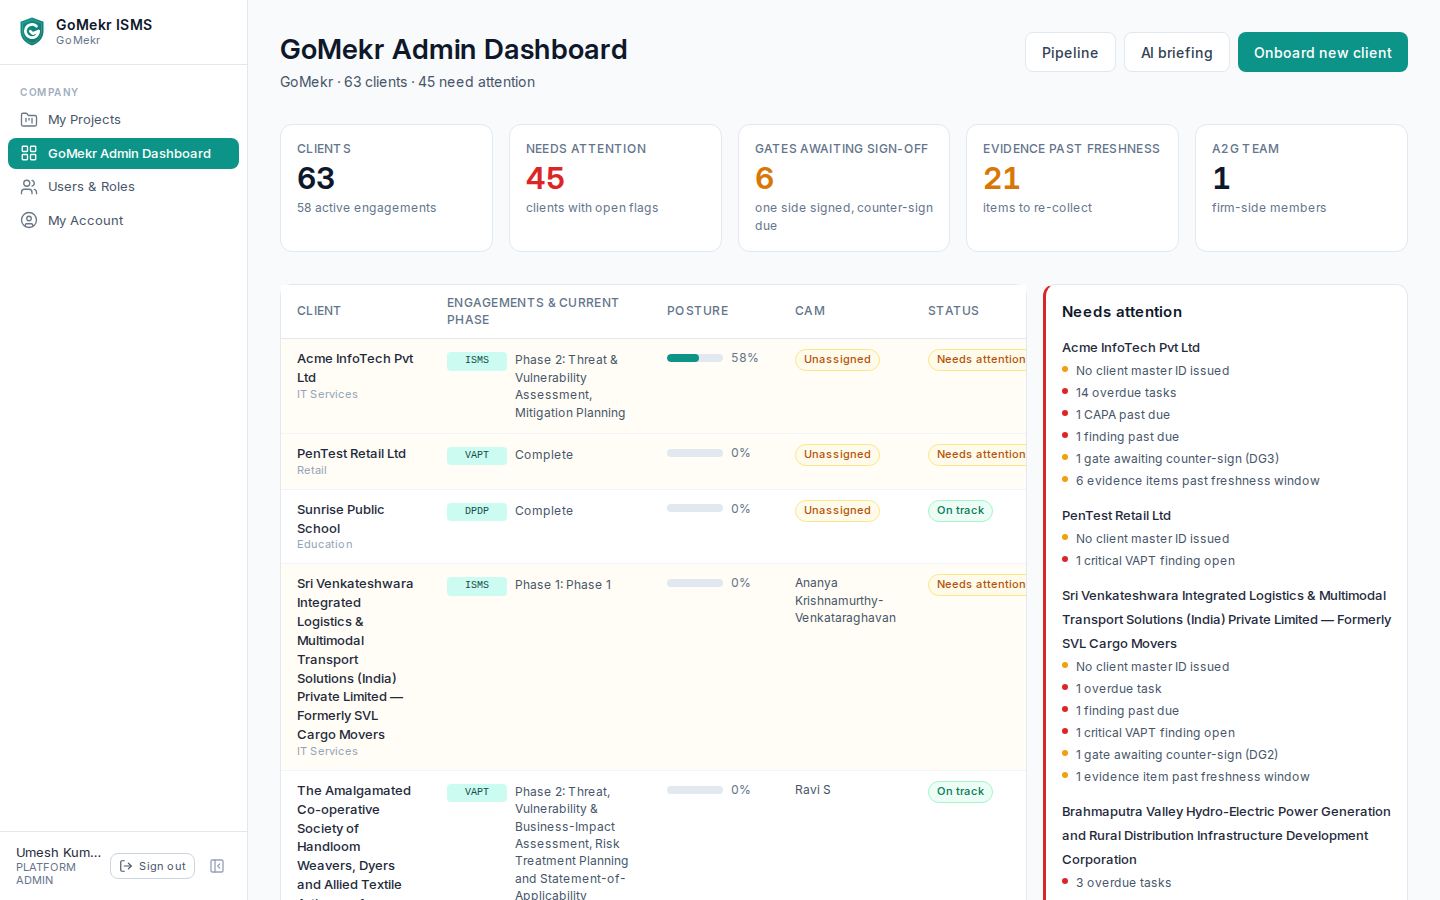
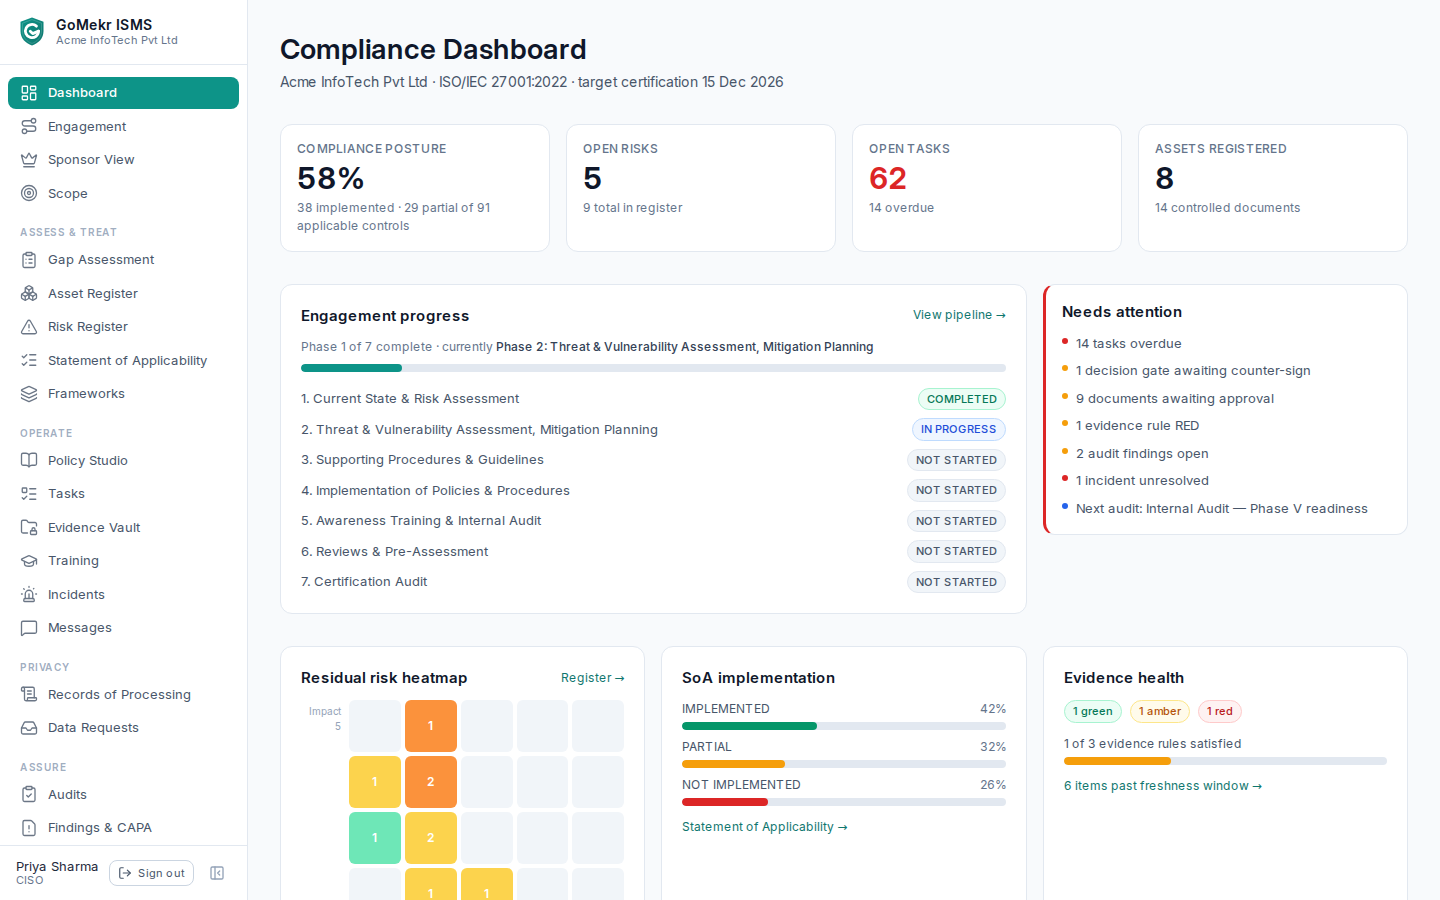
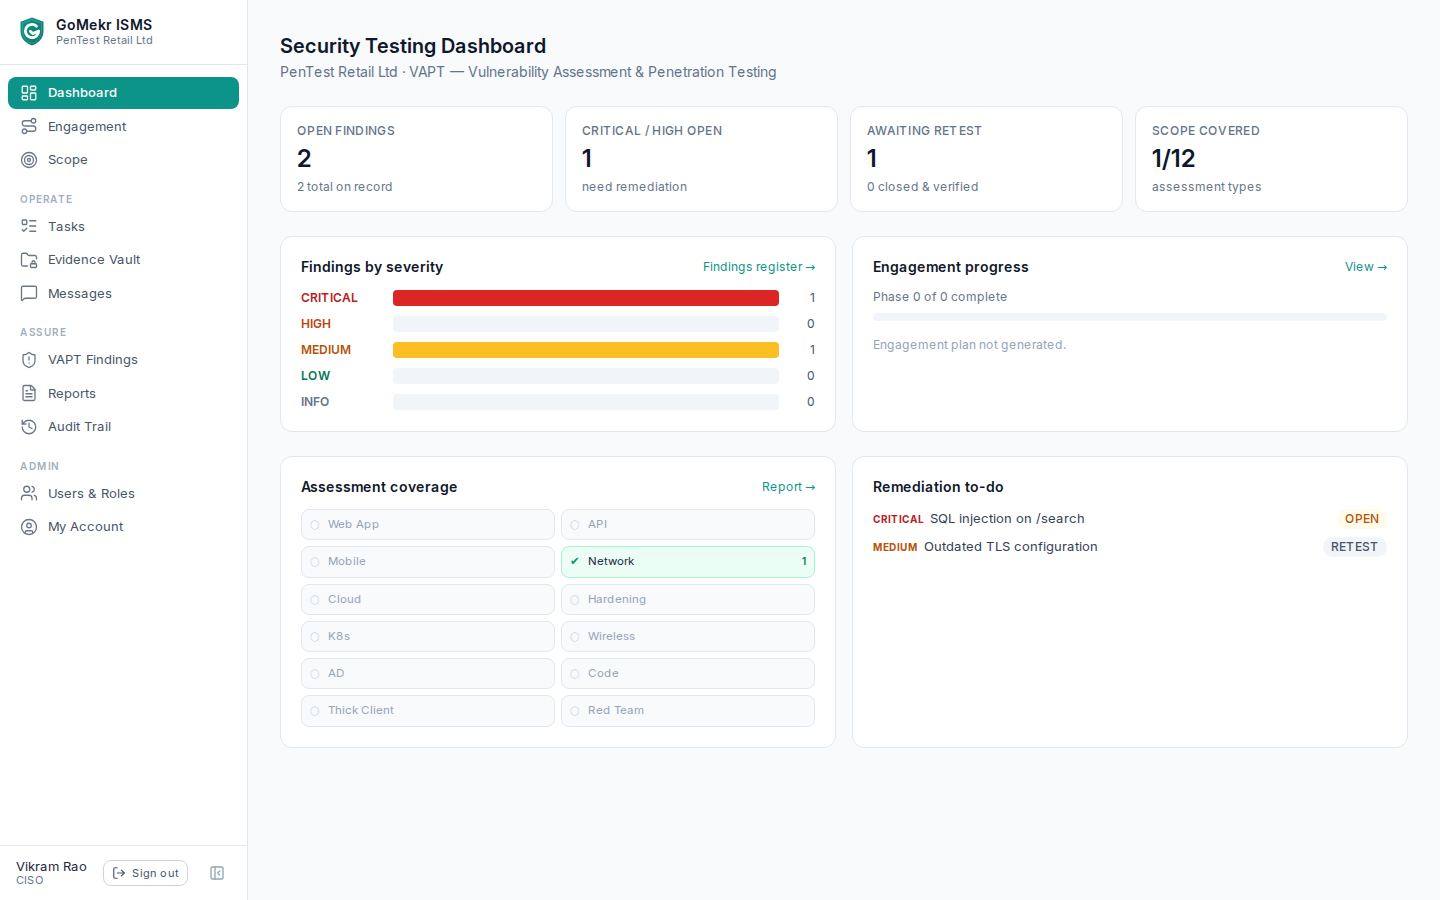
All screenshots show illustrative demo data.
Built like the audit itself
Generic GRC tools track checklists. GoMekr enforces the discipline your external auditor will test you on — sequence, sign-off and sufficiency.
Decision gates neither side can pass alone
Every phase ends in a formal gate — Go, Hold or Rework — with seeded criteria from our methodology. Critical gates require your approver and our reviewer to sign; a premature Go demands a written reason. Every decision is audit-logged.
Evidence sufficiency, computed — never claimed
Nineteen audit-grade rules check your real collection timestamps against required cadence and coverage: access reviews quarterly, restore tests proven, training above 95%. Green, amber or red — with the reason in plain language.
Work that reveals itself in audit order
Tasks are visible from day one but unlock only when their prerequisites are done and the governing gate has passed. Nobody jumps ahead; nobody wonders what is next. Owners are emailed the moment their work becomes actionable.
Every audit, one platform
Each service is a versioned roadmap in our catalog — controls, policies and evidence are shared across frameworks, so every additional certification costs less effort than the last.
ISO/IEC 27001:2022 — ISMS Certification
Our flagship: a 41-activity implementation roadmap across 12 phases with dependency-driven sequencing, 8 decision gates and clause-mapped evidence — from charter to certificate.
ISO 27001 + SOC 2 Type II — Integrated
Comply once, certify twice. One 49-activity roadmap carries you through the ISO certification audit and the SOC 2 Type II examination — one evidence effort, dual coverage.
ISO 9001:2015 — QMS
Quality management certification: process mapping, KPIs, internal quality audits and management review — tracked clause by clause.
Privacy — DPDP Act / GDPR
India DPDP Act 2023 and GDPR readiness: records of processing, consent, breach playbooks and data-principal request handling with due-date tracking.
VAPT
Vulnerability assessment and penetration testing with a live findings tracker — severity, remediation, retest verification and executive reporting.
Outsourced Internal Audit
Risk-based internal audit programs delivered by independent auditors — planning, fieldwork, findings and CAPA follow-through to closure.
The full GRC portfolio
Certification is one destination — governance, risk and compliance is the whole map. Twelve service lines, one delivery team, one governed platform.
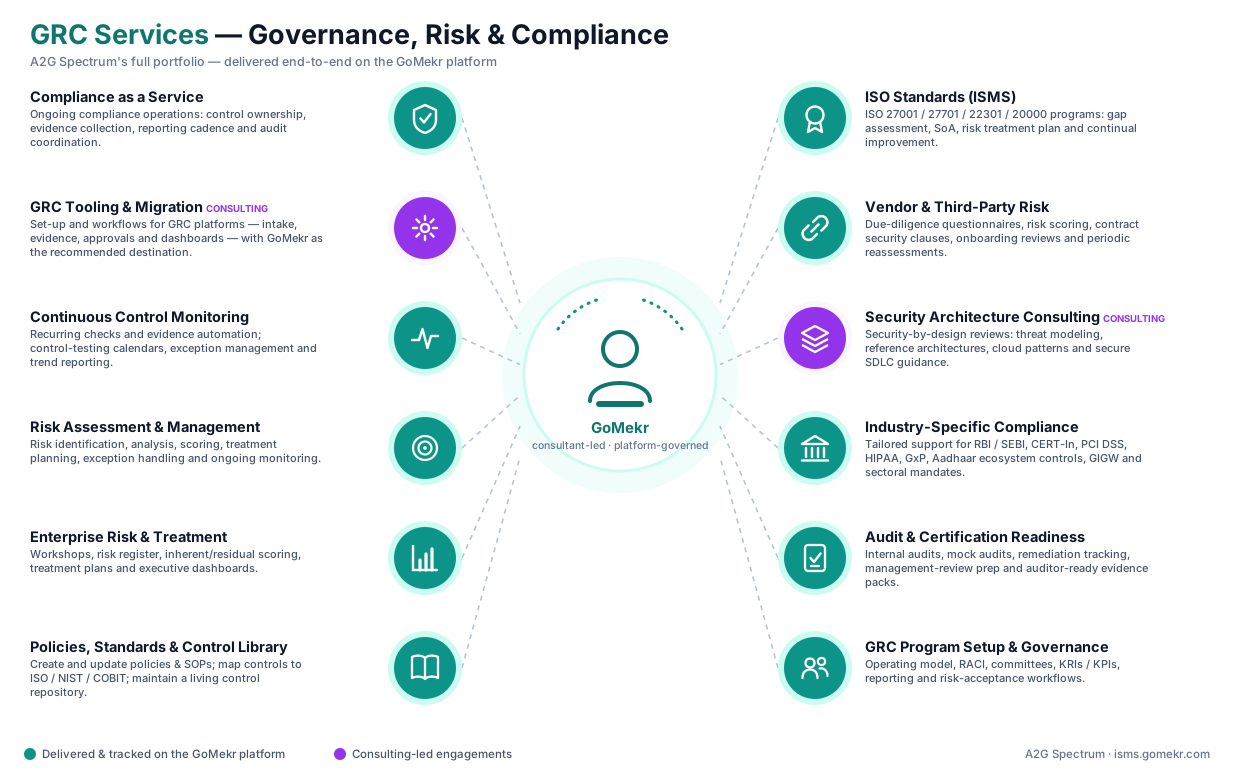
delivered & tracked on GoMekrconsulting-led — every engagement lands in the same governed workspace, so each additional service builds on evidence you already have.
Compliance as a Service
On GoMekrOngoing compliance operations: control ownership, evidence collection, reporting cadence and audit coordination.
Your controls keep running after the certificate: the evidence cadence engine, task routing and weekly digests keep the management system alive between audits — with A2G operating it alongside your team.
GRC Tooling & Migration
Consulting-ledSet-up and workflows for GRC platforms — intake, evidence, approvals and dashboards.
We implement and migrate GRC tooling end-to-end, with GoMekr as the recommended destination: your control library, evidence and history arrive structured, not screenshotted.
Continuous Control Monitoring
On GoMekrRecurring checks and evidence automation; control-testing calendars, exception management and trend reporting.
Every control knows its testing cadence. GoMekr computes sufficiency continuously — GREEN, AMBER, RED per control — so exceptions surface the week they happen, not the week before the audit.
Risk Assessment & Management
On GoMekrRisk identification, analysis, scoring, treatment planning, exception handling and ongoing monitoring.
A living risk register with owners, scores and treatment plans — reviewed on cadence, linked to the controls that treat each risk, visible on the executive dashboard.
Enterprise Risk Assessment & Treatment
On GoMekrWorkshops, risk register, inherent/residual scoring, treatment plans and executive dashboards.
Facilitated workshops feed a register with inherent and residual scoring; the residual heatmap and treatment progress land straight on your leadership's dashboard.
Policies, Standards & Control Library
On GoMekrCreate and update policies & SOPs; map controls to ISO / NIST / COBIT; maintain a living control repository.
Policy Studio gives every document a named owner, version history with dates, an internal review workflow and staff acknowledgments — a living library, not a folder of PDFs.
ISO Standards (ISMS)
On GoMekrISO 27001 / 27701 / 22301 / 20000 programs: gap assessment, SoA, risk treatment plan and continual improvement.
Versioned roadmaps with decision gates and dual sign-off carry each standard from gap assessment to certificate — ISO 27001 today; 27701, 22301 and 20000 on the same engine.
Vendor & Third-Party Risk Management
On GoMekrDue-diligence questionnaires, risk scoring, contract security clauses, onboarding reviews and periodic reassessments.
Tiered vendor assessments with expiry-tracked attestations — one current SOC or ISO certificate per critical vendor, monitored so renewals never lapse silently.
Security Architecture Consulting
Consulting-ledSecurity-by-design reviews: threat modeling, reference architectures, cloud patterns and secure SDLC guidance.
Expert-led design reviews before you build: threat models, reference architectures and secure-SDLC guardrails — deliverables tracked in your engagement workspace.
Industry-Specific Compliance
On GoMekrTailored support for RBI / SEBI, CERT-In, PCI DSS, HIPAA, GxP, Aadhaar ecosystem controls, GIGW and sectoral mandates.
Sectoral mandates mapped onto the controls you already run — regulatory registers, gap views and evidence packs shaped for each regulator's expectations.
Audit & Certification Readiness
On GoMekrInternal audits, mock audits, remediation tracking, management-review prep and auditor-ready evidence packs.
Independent internal audits and mock assessments with findings and CAPA tracked to verified closure — you walk into Stage 2 already knowing the answer.
GRC Program Setup & Governance
On GoMekrOperating model, RACI, committees, KRIs / KPIs, reporting and risk-acceptance workflows.
The operating model installed, not just documented: RACI-routed tasks, steering cadence, KPI packs and dual-approved risk-acceptance workflows running in the platform.
VAPT — the full assessment map
Twelve assessment types under one engagement — and every finding is tagged with the assessment that produced it, so the report shows exactly what scope was covered.
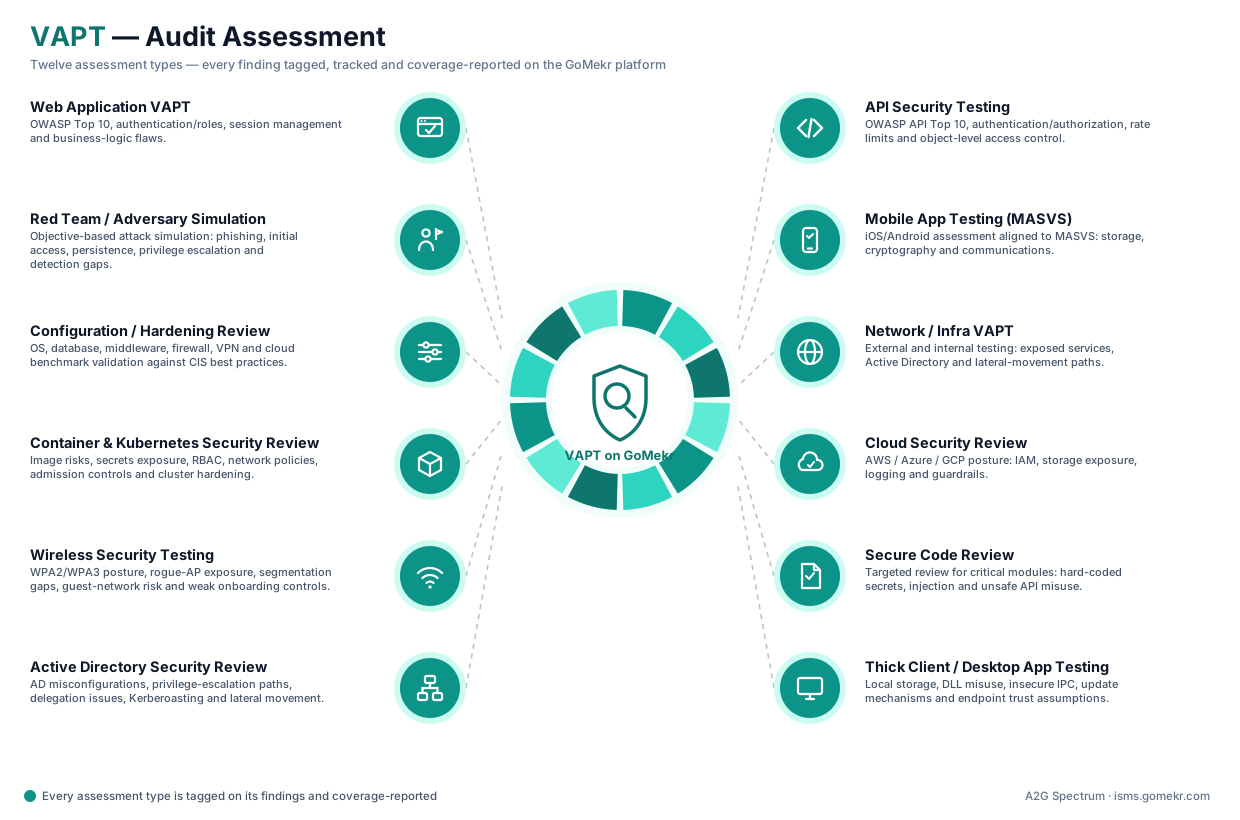
Web Application VAPT
OWASP Top 10, authentication and roles, session management and business-logic flaws.
API Security Testing
OWASP API Top 10, authentication/authorization, rate limits and object-level access control.
Mobile App Testing (MASVS)
iOS/Android assessment aligned to MASVS: storage, cryptography and communications.
Network / Infra VAPT
External and internal testing: exposed services, Active Directory and lateral-movement paths.
Cloud Security Review
AWS / Azure / GCP posture: IAM, storage exposure, logging and guardrails.
Configuration / Hardening Review
OS, database, middleware, firewall, VPN and cloud benchmark validation against CIS best practices.
Container & Kubernetes Review
Image risks, secrets exposure, RBAC, network policies, admission controls and cluster hardening.
Wireless Security Testing
WPA2/WPA3 posture, rogue-AP exposure, segmentation gaps, guest-network risk and weak onboarding.
Active Directory Security Review
AD misconfigurations, privilege-escalation paths, delegation, Kerberoasting and lateral movement.
Secure Code Review
Targeted review for critical modules: hard-coded secrets, injection and unsafe API misuse.
Thick Client / Desktop App Testing
Local storage, DLL misuse, insecure IPC, update mechanisms and endpoint trust assumptions.
Red Team / Adversary Simulation
Objective-based attack simulation: phishing, initial access, persistence, escalation and detection gaps.
From kick-off to certificate
A named account manager and subject-matter experts work inside the platform with you — every phase, decision and message in one governed place.
01
Onboard
From engagement confirmation to a provisioned workspace in a day — team mapped, roadmap instantiated, stakeholders invited.
02
Plan
One click generates your full task plan: every activity routed to its owner on your side or ours, in dependency order.
03
Deliver
Work unlocks as predecessors finish and gates pass. Evidence is collected against audit-grade cadence rules.
04
Certify
Dual-signed gates, a defensible audit trail and a certification-ready evidence vault — then stay compliant, cycle after cycle.
Visibility without chasing
Your leadership always knows where it stands
- ✓
The Sponsor view
One screen for your executives: readiness, phase progress, gate status, overdue work and evidence health — read-only, always current, never self-reported.
- ✓
The Monday digest
Every week, engagement leadership receives the computed status by email: what moved, what is waiting, what needs attention. No status meetings required.
- ✓
Least-privilege by design
Access is granted per process, per engagement. Our account managers coordinate but cannot touch delivery; our auditors cannot edit what they audit. Any exception needs approval from both sides — and everything is logged.
- ✓
A defensible audit trail
Gate decisions, early sign-off reasons, access changes and denials — recorded with who, what and when. Your certification evidence includes the story of how you got there.
Weekly status 64% — your engagement
Mon 9:00Overall readiness: 64% (26/41 activities done)
Current phase: P7 Operate & Evidence
Gates: ✔ DG0 ✔ DG1 ✔ DG2 ✔ DG3 ✔ DG4 · DG5 · DG6
Work in play: 7 active · 1 overdue
Evidence health: 82% (14 green · 3 amber · 2 red)
Waiting on:
• IT Head — 3 active tasks
• ISMS Manager — 2 active tasks
Needs attention:
! KPI packs — 1 month gap in coverage
! Vendor attestations — nothing on file
Which audit is next for your business?
Talk to an A2G Spectrum expert. Your workspace can be live within a day of confirming the engagement — and your leadership will see the compliance picture from week one.